A Fake Interview, a $6.34 Billion Heist: How Binance Was Breached
Binance has confirmed the theft of approximately $6.34 billion in a sophisticated social-engineering campaign that unfolded over several months. The attack began with a fake job interview — a now-familiar lure in which targets are invited to a video call and asked to install software or share screen access under the guise of a technical assessment. US authorities have attributed the operation to the North Korean state-linked group TraderTraitor, also known as Lazarus Group. Kim Yo-jong, deputy director of North Korea’s propaganda department, denied the allegation, calling it a baseless smear.
Anatomy of the Attack
The breach was not a single exploit but a patient, multi-stage intrusion. The attackers:
- Used AI-generated personas and deepfake video to conduct convincing interviews with Binance employees and contractors.
- Deployed malware disguised as productivity or interview-prep tools to establish initial access.
- Moved laterally across internal systems over weeks, mapping wallet infrastructure and approval workflows.
- Executed withdrawals in carefully structured tranches designed to evade automated anomaly detection.
The scale — over $6 billion — dwarfs most DeFi exploits and exchange hacks combined. It is a stark reminder that the weakest link in crypto security remains the human layer, not the smart contract layer.
Why This Matters for the Industry
Binance has launched a remediation program, but the incident raises uncomfortable questions for every exchange and custodian. AI has collapsed the cost of running convincing social-engineering campaigns. Deepfaked video calls, synthetic voices, and LLM-crafted phishing emails mean that the traditional security playbook — employee training, email filters, and two-factor authentication — is no longer sufficient. Firms must now assume that any inbound communication could be adversarial and that identity verification must be continuous, not one-time.
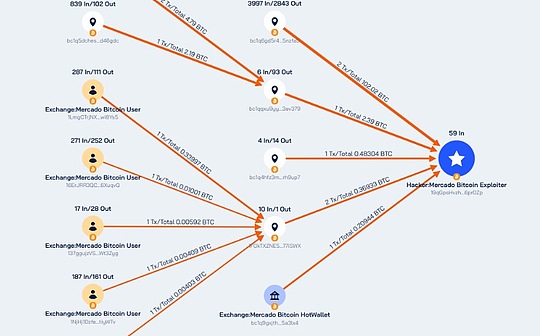
The geopolitical dimension is equally significant. TraderTraitor has been linked to multiple crypto thefts, and the funds are often laundered through mixers, chain-hopping bridges, and over-the-counter desks. The denial from Pyongyang is predictable, but the on-chain evidence trail will be critical. Exchanges and analytics firms will need to coordinate closely to freeze or recover assets — a process that is slow, partial, and politically fraught.
Forward-Looking Perspective
The Binance incident is likely to accelerate three trends: stricter operational-security standards for exchanges, greater adoption of hardware-based multi-party computation (MPC) custody, and regulatory pressure for mandatory incident disclosure. It also strengthens the case for AI-powered defensive tools — anomaly detection that can spot unusual approval patterns in real time. For the industry, the lesson is clear: as AI lowers the cost of deception, the cost of trust must rise. The next wave of exchange security will be defined not by firewalls, but by verified human identity and zero-trust architecture.